 Security Product Engineering


Security Product Engineering for Cybersecurity and AI Companies
Deep security domain understanding and engineering discipline to build at speed, at scale, without compromising quality, so you ship with confidence.
Trusted by leading ISVs
and ecosystem partners

Engineering Challenges Unique to Security Software
Security products bring constraints most engineering teams never encounter. Software quality, adversarial QA, security product scalability, and technical debt each carry consequences that reach customers. Five pressures shape how security products get built.
 Speed vs. Depth — Ship fast without creating security debt Domain Complexity — IAM, detection, threat intelligence, and AI require specialist knowledge Adversarial QA — Test beyond standard functional scenarios Secure Scale — Maintain isolation, performance, and control as adoption grows AI Attack Surfaces — Secure new GenAI and agentic AI risks
Security Product Engineering Services
Cybersecurity product engineering, ecosystem integrations, AI security product engineering, adversarial QA, and DevSecOps for companies whose product is the security layer.
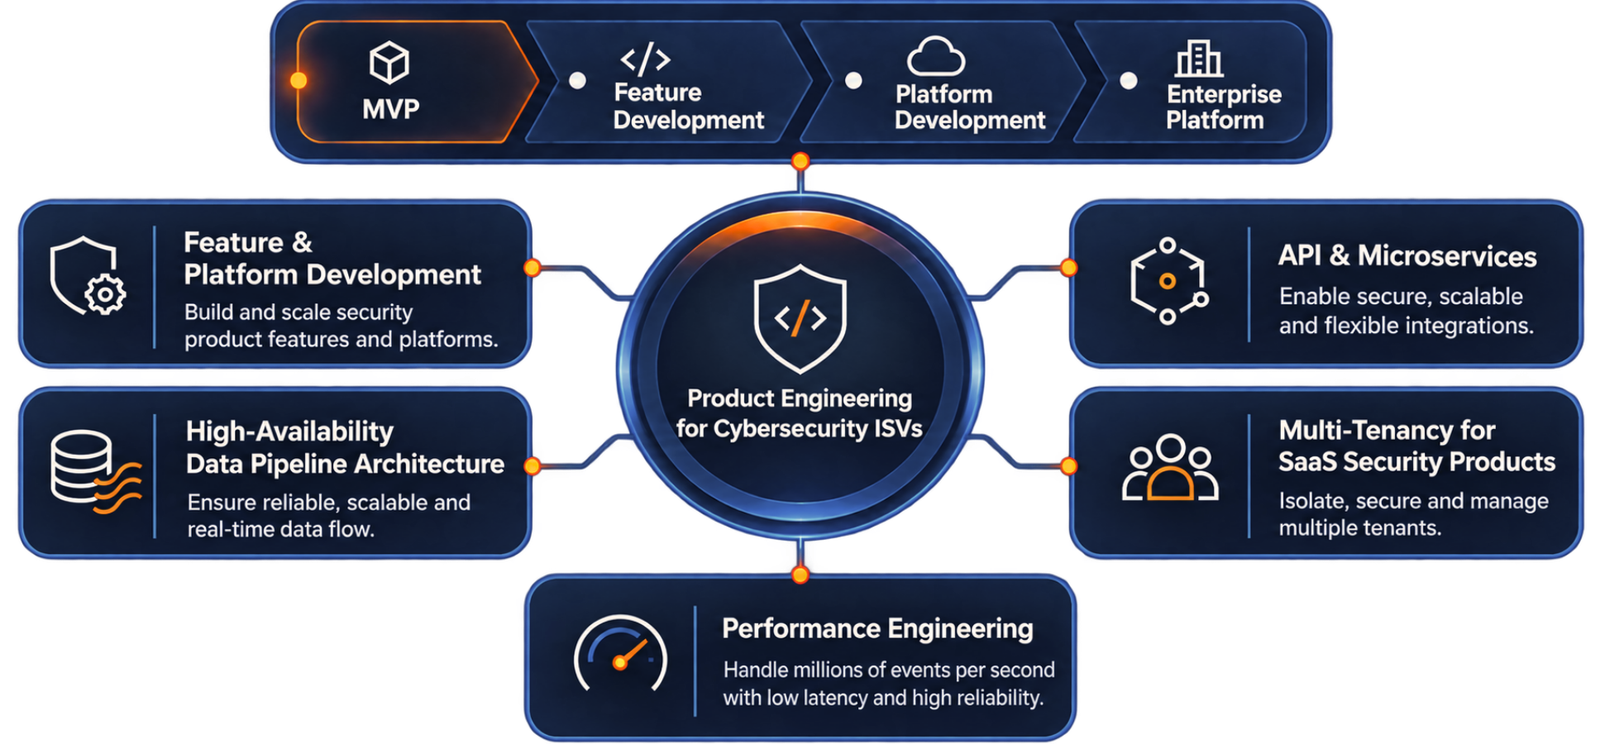
Security product engineering from early-stage MVPs to enterprise-grade platforms. Engineers understand security architecture, not just software architecture. Coverage includes feature development and platform engineering, high-availability and low-latency security data pipeline architecture, API and microservices development, and multi-tenancy engineering for SaaS security products. Performance engineering supports millions of events per second, while technical debt remediation helps systems built fast scale safely
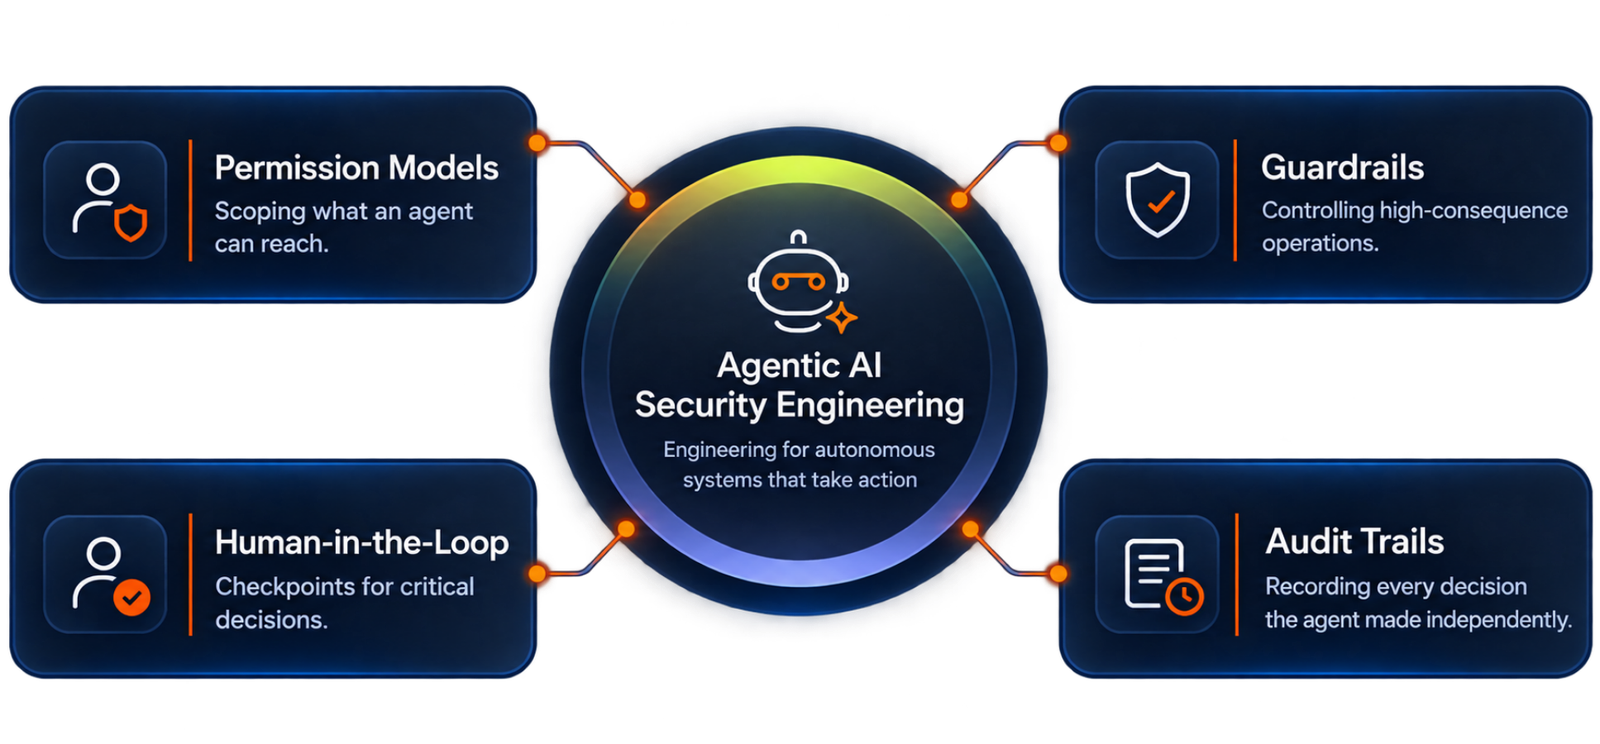
The AI Security space is moving faster than any other in cybersecurity. We provide product engineering for AI security, agentic AI and GenAI security products, including LLM security for prompt injection detection, context security and output filtering; RAG security for enterprise deployments; and agentic AI security for autonomous AI systems, with MCP/tools call controls, guardrails, permission models and audit trails. We also build AI/LLM gateways, AI observability, and model security tooling.
Security product QA finds what attackers find—before they do. We combine security-aware functional testing for adversarial edge cases, penetration testing integration, red-team thinking, and Agent Testing / QA. Compliance-driven QA maps coverage to SOC 2, ISO 27001, FedRAMP and HIPAA. Performance and load testing validates real-world volumes, while AI/LLM QA covers hallucination, prompt injection and context boundaries, plus regression testing for model drift that silently changes security behavior.
Security products live in ecosystems. We build native integrations across SIEM, SOAR, IAM, PAM, EDR and XDR, plus cloud and SaaS integrations for AWS, Azure, GCP, EC2, S3, RDS and CloudWatch. Marketplace integration development covers Splunk, Microsoft Sentinel, CrowdStrike and ServiceNow. We also integrate threat intelligence feeds using STIX/TAXII, MISP and VirusTotal, identity systems with SCIM, LDAP, Okta, Azure AD, Entra and WorkOS, and manage partner ecosystem connector library management.
Your CI/CD pipeline must be as secure as the product it ships. We deliver DevSecOps practices purpose-built for security product engineering, embedding SAST, DAST and SCA into security-native CI/CD pipelines at every stage. Coverage includes secrets management, supply chain security and SBOM practices; container and image hardening for security product deployments; compliance-as-code with automated policy gates for regulatory requirements; and end-to-end secure SDLC design, implementation, and secure delivery.

Roadmap Partnership
Growth from MVP to
enterprise platform
Shipped Without Debt
No shortcuts returning
as vulnerabilities
Capacity Without Hiring
Scale without onboarding
or management
Faster AI Releases
Shipped without cutting
security corners
Roadmap That Grows
From first AI feature
to full platform
AI Depth On Demand
Specialist skills
without hiring for them
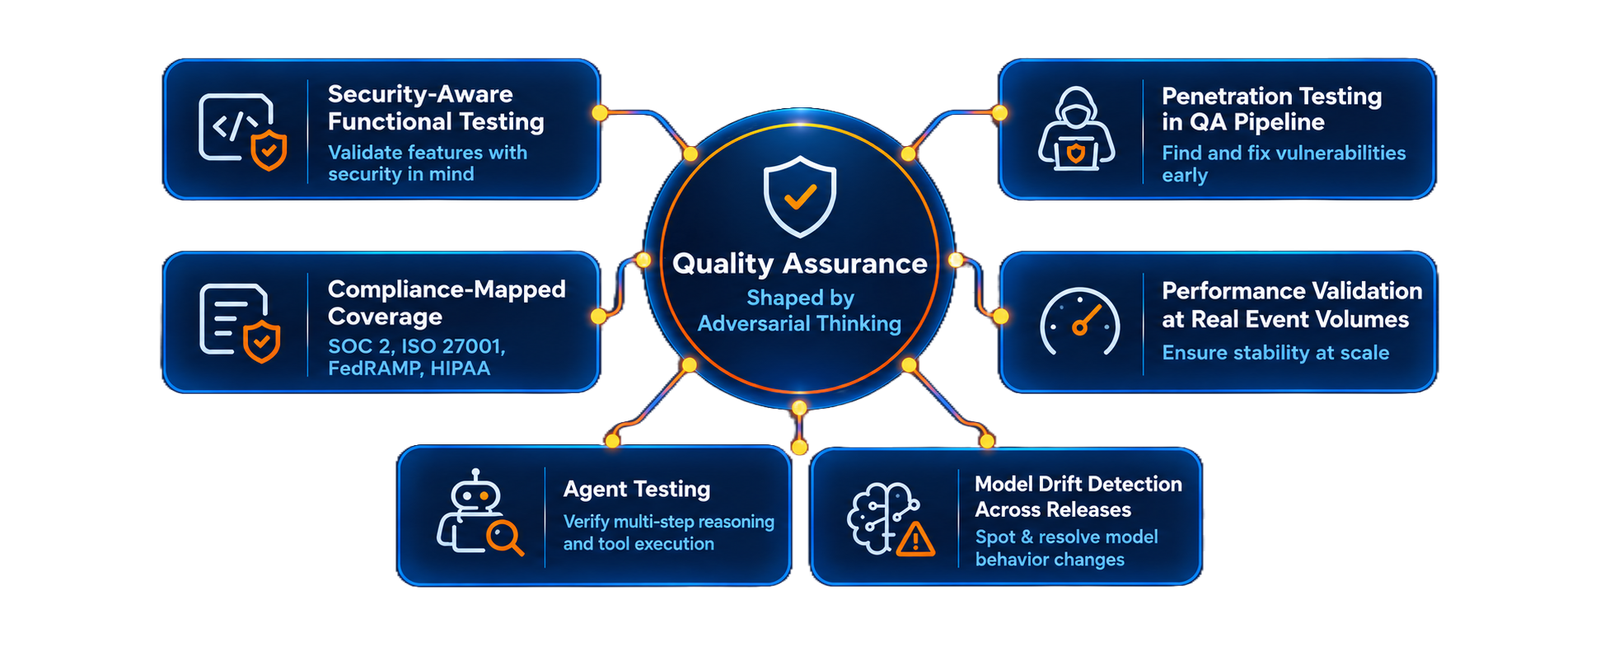
Attacker-Level Coverage
Issues found before
customers ever see them
Release Confidence
Shipped without
trading away quality
QA Capacity On Tap
Test scale without
hiring or onboarding
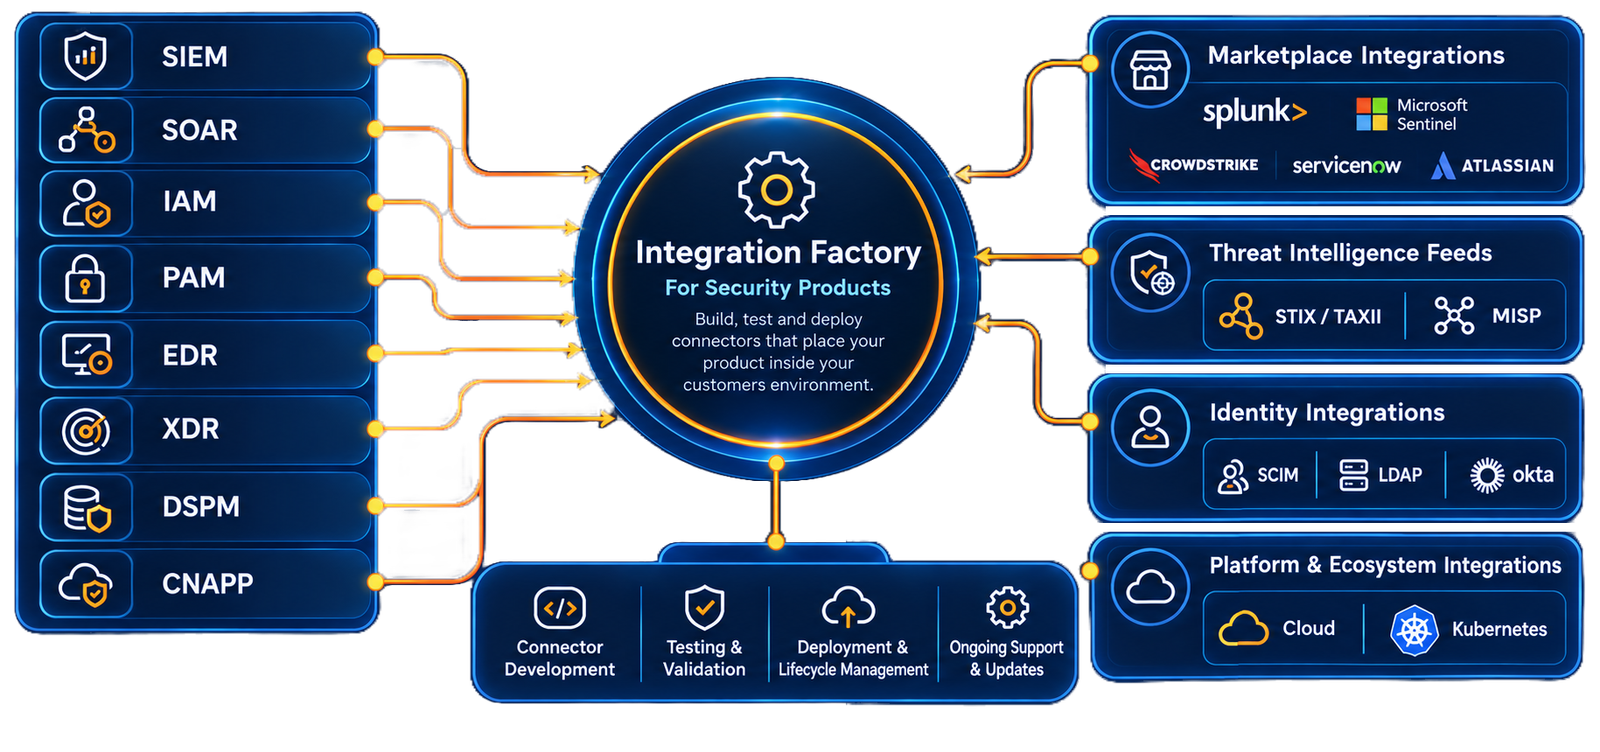
GTM Acceleration
Integration ecosystems
that win enterprise deals
Enterprise Deals Won
Native integrations
enterprise buyers expect
Connector Scale
Growth without adding
connector headcount
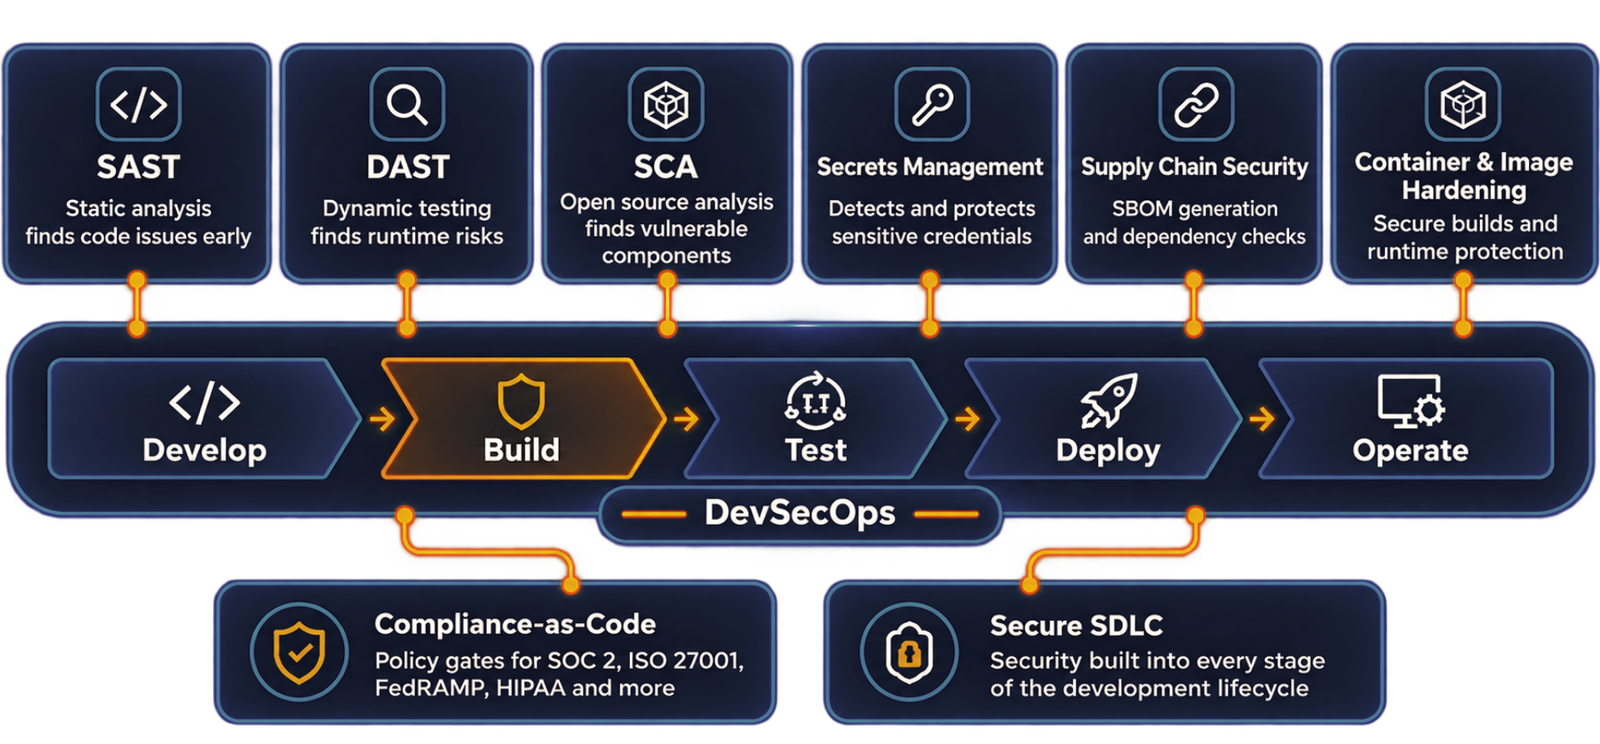
Pipeline Ships Faster
Secure releases
without cutting corners
Compliance Without Delay
Regulatory gates that
never block delivery
DevSecOps Capacity
Practice depth without
hiring overhead
Our Technology Ecosystem
Deep working knowledge across the security platforms, AI frameworks, and DevSecOps tooling that modern security products depend on.
Languages


AI and LLM

Security Platforms
Opensource Tech
QA and Testing
DevSecOps
Cloud

Containers

Observability
Integration

Building a Cybersecurity Product?
Tell us what you're building, where you're stuck, or what capability you need to add. We'll get into the security product engineering and work out what it takes to move forward.
Built for Security-First Product Companies
Opcito helps security software companies build the products their customers rely on to strengthen their security posture. That means engineering secure, scalable products that can meet the demands of enterprise environments.
Building EDR, CNAPP, CSPM, DSPM, IAM, PAM, XDR, vulnerability management, or threat intelligence platforms.
Building products that secure AI systems, detecting model misuse, protecting inference pipelines, governing AI access, and monitoring model behaviour in production.
Building autonomous agents that make security decisions or execute remediation, with permission scoping and explainability.
Building prompt injection detection, RAG security, LLM firewalls, and content guardrails for generative systems.
Holding a clear product vision, needing engineering capacity that keeps architecture intact as the customer base grows.
Why Opcito for Security Product Engineering
There’s a difference between understanding security and engineering within the security domain every day. We apply that depth across the products we build and test, from cybersecurity and AI Security to GenAI and agentic AI platforms.
Security Domain Fluency
Threat vectors, attack surfaces, CVEs, MITRE ATT&CK, OWASP LLM Top 10. You won't spend time explaining your domain to us before we can start solving the engineering problem.
Attacker Mindset, Engineering Discipline
Our QA and engineering mindset is adversarial by default. We look for what breaks, where it breaks, and what it takes to make the product stronger.
AI Security
Expertise
We've been working in AI Security long enough to understand the engineering realities behind the hype, with strong opinions on what works, what doesn't, and where the real risks lie.
Focused Partner, Not a Large SI
You get engineers who are accountable for outcomes, without layers of delivery management between you and the people building the product.
Extension of Your Engineering Team
We align with your roadmap, sprint cadence, architecture decisions, and quality bar, working within your engineering process rather than around it.
Built for Complexity. Engineered for Scale.
Building the technology capabilities that underpin enterprise scale and resilience.
Secure, Multi-Region Internal Developer Platform for a Global Data…
Centralized identity integration for a cybersecurity platform
Enhancing security solutions for a K8s-based security startup
Real-time monitoring automation for a security solution
Frequently Asked Questions
Quick answers to your most common questions around Security Product Engineering.
At Opcito, we see security products operating under different engineering pressures. Teams need to move quickly without creating security-sensitive technical debt, work across IAM, detection, threat intelligence and AI attack surfaces, test against adversarial behaviour, and maintain security as customer and data volumes grow.
Opcito works with cybersecurity ISVs and product companies, AI Security product companies, Agentic AI Security companies, GenAI Security platform companies, and security startups scaling their products. These include companies building areas such as EDR, CNAPP, CSPM, DSPM, IAM, PAM, XDR, vulnerability management, threat intelligence, AI security and GenAI security platforms.
Opcito supports feature and platform engineering, security product architecture, APIs and microservices, multi-tenant SaaS engineering, performance engineering and technical debt remediation. The focus is on building and scaling security products from early-stage MVPs to enterprise-grade platforms.
Opcito supports LLM security engineering, RAG security, Agentic AI security, AI/LLM gateways, AI observability and model security tooling. This includes areas such as prompt injection detection, context security, output filtering, tool-call controls, guardrails, permission models, audit trails, model routing and adversarial testing.
Opcito applies security-aware QA with an adversarial mindset rather than relying only on standard functional testing. The scope includes security-focused functional testing, penetration-testing integration, red-team thinking, compliance-driven QA, performance and load testing, AI and LLM-specific QA, model-drift regression testing and agent testing.
Opcito supports security software product companies across security platform architecture, connector development, QA, and DevSecOps. Engagements can range from an embedded engineering team working within your roadmap to scoped project delivery for specific product capabilities.
Have a Security Engineering Challenge?
Whether it's detection, security automation, AI security, GenAI, or a complex integration, bring us the problem. We'll work through the engineering and figure out where we can help.